AI SECURITY
Protect AI models, enterprise data, AI applications, and autonomous agents across development and runtime. AppXcess delivers dedicated AI security solutions that defend against prompt injection, sensitive data leakage and model misuse, reducing the security, privacy, governance and compliance risk that comes with enterprise AI.
Protect AI Models
Guard model weights, fine-tuning datasets, and inference pipelines against data poisoning, weight extraction, and model tampering.
Shield Enterprise Data
Prevent confidential records, IP, credentials, and sensitive PII from leaking into prompts or outbound generated responses.
Secure AI Applications
Deploy runtime guardrails, prompt validation firewalls, and isolated execution boundaries for enterprise LLM apps.
Govern AI Agents
Enforce least-privilege tool execution, human-in-the-loop validation checkpoints, and verifiable immutable audit trails.
AI-Specific Security Risks
Modern AI environments introduce distinct threat vectors beyond standard network perimeters. AppXcess systematically addresses each AI-native vulnerability through the framework of Risk → Protection → Business Impact.
Prompt Injection & Jailbreaks
Malicious prompt sequences that manipulate model reasoning, bypass system instructions, hijack application logic, or trigger unauthorized downstream tool calls.
Multi-layer token inspection, adversarial prompt sanitization, semantic similarity evaluation, and pre-execution guardrail firewalls before inference.
Prevents application hijacking, unauthorized data extraction, logic manipulation, and brand damage caused by adversarial user prompts.
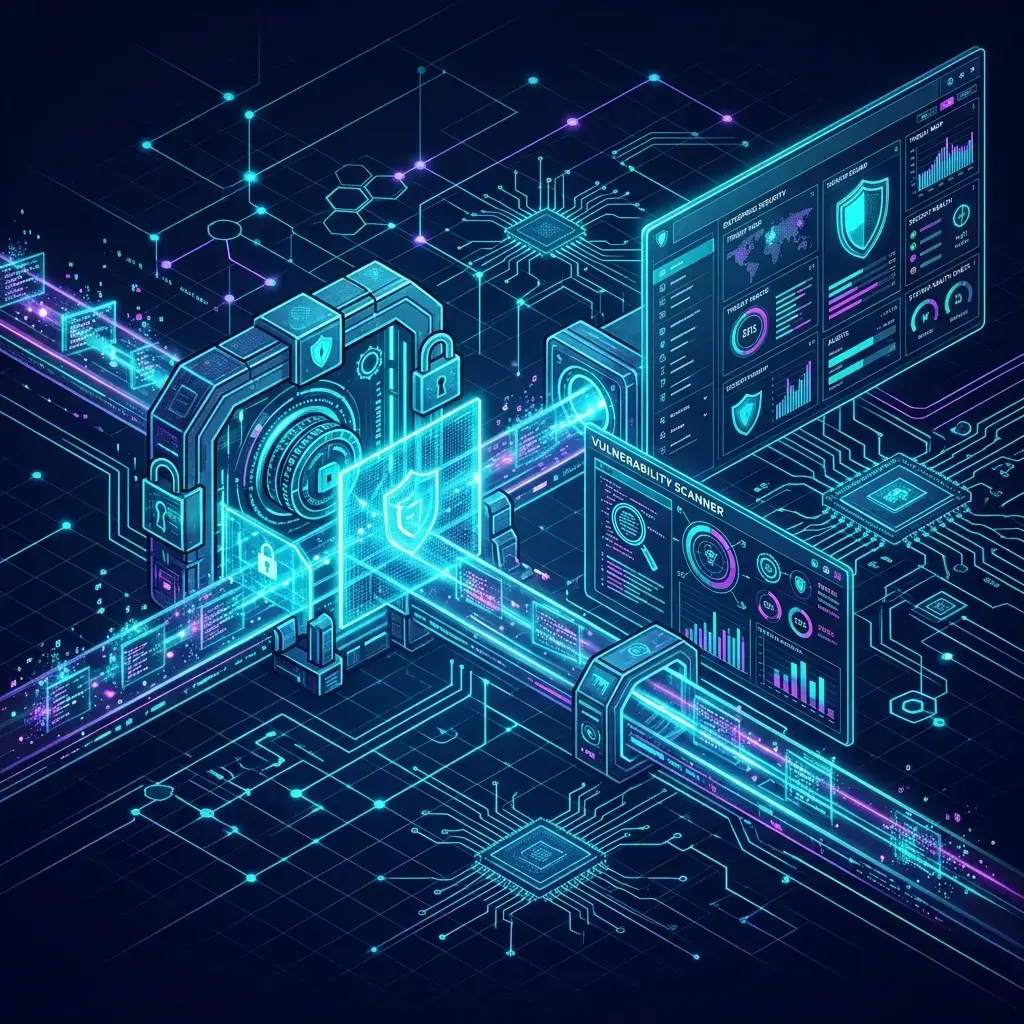
Active defense layers mitigating prompt injection & jailbreaks across enterprise AI inference pipelines.
AI Security Monitoring
Continuously monitor AI systems to detect unusual prompt patterns, token extraction spikes, policy violations, and model drift before they compromise business operations.
Threat Intelligence
Detect adversarial prompt spikes, extraction probing, and emerging AI attack patterns.
Compliance Oversight
Monitor governance controls, data boundary enforcement, and continuous audit readiness.
Runtime Visibility
Track model execution activity, token throughput, API traffic, and latency telemetry.
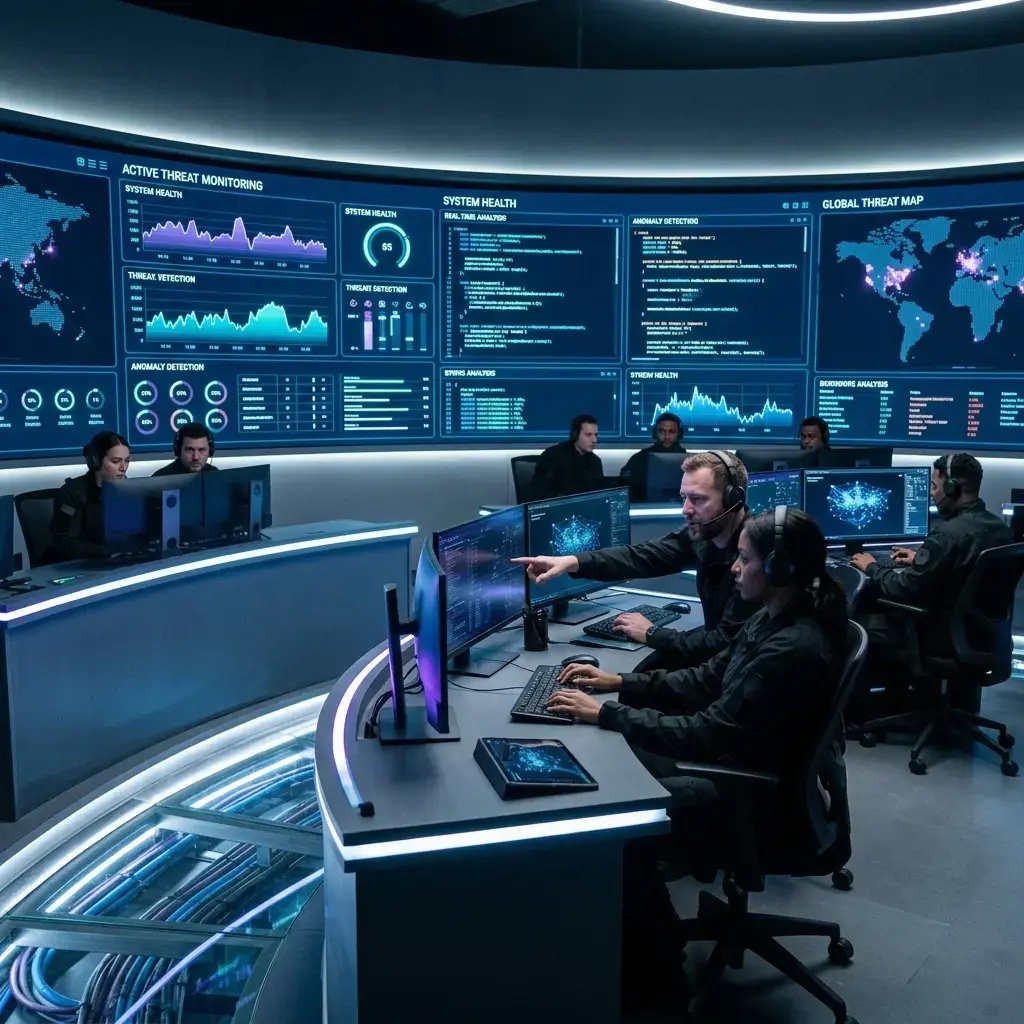
Continuous Visibility
Track model telemetry logs, API routing patterns, and data pipeline compliance levels proactively.
Risk Detection
Isolate prompt spikes, token anomalies, and evasion attempts before models are impacted.
Policy Monitoring
Verify query outputs against regulatory data limits and internal safety guidelines automatically.
AI Runtime Security
Secure AI execution environments, model interactions, and operational workflows with strict runtime containment and bidirectional guardrails.
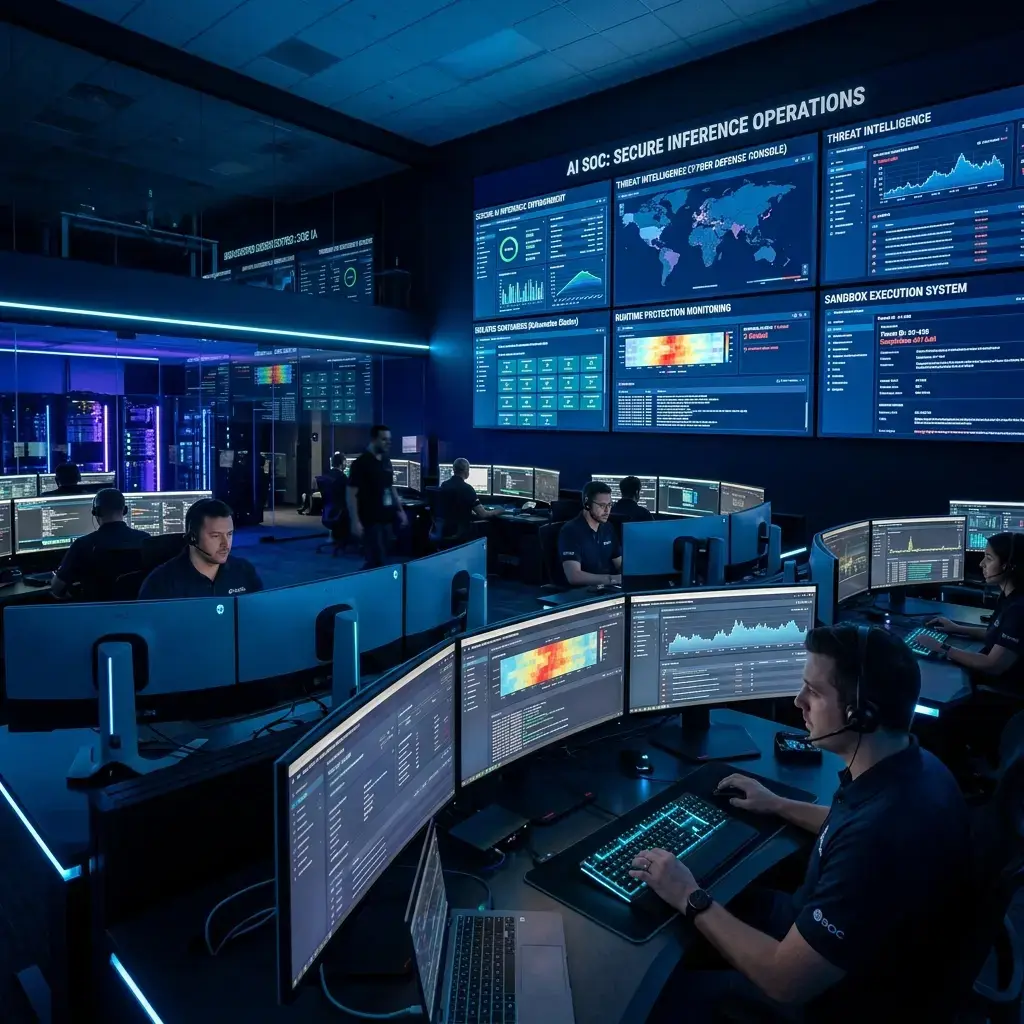
AI Guardrails & Validation
Enforce low-latency bidirectional inspection gates to intercept adversarial prompts and filter toxic model outputs before rendering.
Secure Inference & Sandboxing
Run inference inside isolated execution environments, so a query and its logs stay within the boundary you set for them.
Role-Based Access Controls
Map active model permissions dynamically across teams, restricting model invocation and fine-tuning datasets to verified credentials.
Security Capabilities & Governance
Enterprise security controls must serve a clear business purpose. Every capability supported by AppXcess is organized around Risk → Protection → Business Outcome, linking technical enforcement directly to enterprise risk reduction.
Role-Based Access Control (RBAC)
Privilege escalation and unauthorized personnel invoking sensitive models or proprietary datasets.
Granular RBAC and ABAC policies synchronized with enterprise identity systems (SSO/IAM) governing model access.
Restricts model invocation and data access strictly to authorized business functions.
Data & Model Encryption
Interception or extraction of prompt payloads, vector embeddings, and proprietary weights in transit or at rest.
Encryption in transit and at rest across model repositories, vector stores and API traffic, using the mechanisms your platforms provide.
Keeps prompt content, embeddings and model files unreadable to anyone outside the systems you authorise.
Bidirectional AI Guardrails
Prompt injection attacks reaching models and toxic, hallucinatory, or non-compliant outputs reaching users.
Low-latency ingestion sanitization and output validation checks enforcing corporate safety policies.
Keeps model inputs and outputs inside the brand, legal and safety boundaries you define.
Continuous Telemetry & Monitoring
Stealth extraction attacks, behavioral drift, token quota abuses, and latency degradation going unnoticed.
Real-time sensory telemetry tracking query patterns, token consumption, and anomalous execution spikes.
Delivers rapid situational awareness and proactive incident escalation for security teams.
Immutable Audit Trails
Inability to substantiate model decision histories, tool invocations, or policy compliance during formal audits.
Time-stamped, tamper-evident audit logs capturing prompts, model completions, versions, and policy approvals.
Produces defensible, verifiable evidence for compliance reviews and internal accountability.
Governance & Regulatory Support
Non-compliance with evolving global AI regulations, shadow AI adoption, and unvetted model deployments.
Centralized AI model registry, automated policy checks, and alignment with NIST AI RMF and ISO/IEC 42001 principles.
Gives your compliance programme the registry, policy checks and evidence it needs, while certification stays with your auditors.
Enterprise Use Cases
Practical security implementations designed for enterprise buyers. Structured as Business Problem → AI Security Approach → Outcome to deliver verified security value.
Securing Enterprise AI Platforms
Consolidated enterprise AI platforms connecting multiple business tools face risks of credential leakage, unauthorized cross-department data access, and unmonitored usage.
Centralized security monitoring, multi-tenant workspace isolation, unified RBAC mapping, and comprehensive API telemetry tracking.
A secure, centrally governed platform where teams safely collaborate across departments with strict data boundaries.
Protecting LLM Applications
Customer-facing and internal LLM chatbots are vulnerable to prompt injection, confidential document exfiltration, and generating toxic or hallucinatory responses.
Bidirectional runtime guardrails, prompt sanitization firewalls, and factuality citation verification integrated directly into inference pipelines.
Trustworthy LLM applications that maintain customer confidence, brand protection, and compliance with corporate guidance.
Securing AI Agents
Autonomous agents with access to ERP, CRM, databases, and financial systems risk executing unintended, destructive, or unauthorized tool transactions.
Scoped tool permissions, runtime parameter verification, session-isolated credentials, and mandatory human-in-the-loop approvals for high-impact actions.
Agents that speed up workflows while the actions they can take stay bounded, reviewable and reversible.
Protecting Sensitive Business Data
Employees interacting with AI tools inadvertently paste financial forecasts, proprietary code, customer records, and PII into prompts.
Automated DLP scrubbing, context anonymization, real-time PII redaction, and local vector index isolation before queries reach models.
Sensitive records stay inside your boundary, without taking the AI tools away from the people who need them.
Securing Private & On-Premise Deployments
Regulated organizations in healthcare, finance, and the public sector require on-premise or sovereign AI to prevent data from leaving their controlled perimeter.
Isolated execution for model workloads, encryption of local vector stores, and monitoring that runs inside the same perimeter as the deployment.
Model weights and sensitive data stay inside infrastructure you control, with access recorded.
Autonomous Security Operations
Enable intelligent security workflows that automatically detect, investigate, prioritize, and respond to AI-related risks in real time.
Automated Detection
Recognize adversarial prompt injections, anomalous query bursts, and policy violations across API logs instantly.
Intelligent Response
Deploy containment sandboxes, isolate malicious sessions, and throttle anomalous token consumption automatically.
Security Coordination
Dispatch structured security incident tickets, audit traces, and compliance alerts to governance and SOC teams.
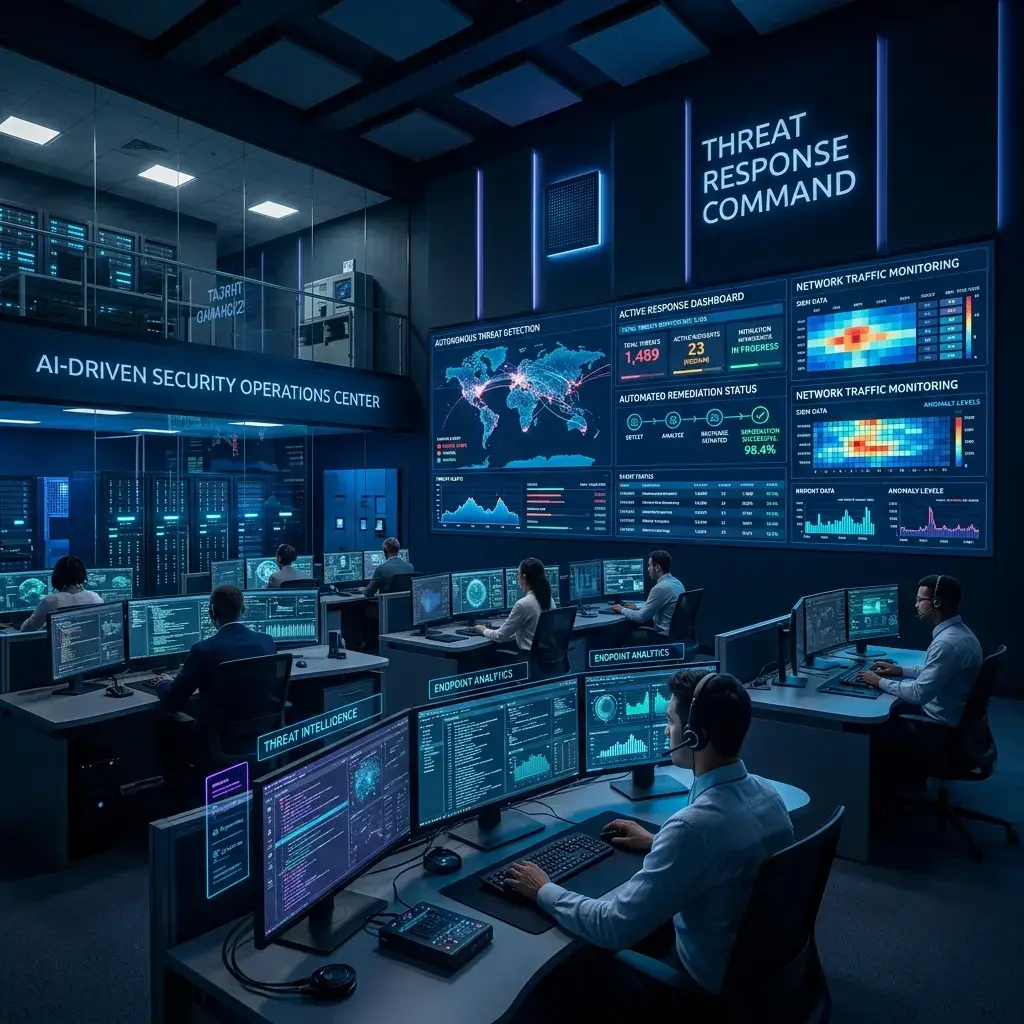
Real-time containment sandboxes, automated query telemetry validation.
Integrated security incident logs, auditable model compliance ledgers.
Reduces manual triage overhead and accelerates threat containment workflows across enterprise AI pipelines.
Security Architecture
Design resilient AI environments with layered security controls embedded across infrastructure, models, applications, and operational workflows.
Infrastructure Security
Run model workloads in isolated environments with the network and access boundaries your infrastructure team defines.
Model Protection
Check model files against a known-good record before they load, so an altered or swapped model is caught rather than served.
Operational Security
Rate-limit inference APIs, scope credentials to a session, and monitor traffic so unusual usage surfaces while it is happening.
Layered pipeline architecture, active cryptographic weight validation.
Integrated architecture security matrix, zero external perimeter vulnerabilities.
Layered controls across the environment, the model files and the queries running against them.
Understanding AppXcess Security & AI Capabilities
AppXcess provides distinct, interconnected solutions tailored to specific enterprise needs. Compare our dedicated offerings below to select the right capability for your organization:
AI Security
Dedicated protection for AI models, AI applications, autonomous agents, enterprise prompts, model outputs, and AI governance frameworks.
AI guardrails, prompt sanitization, agent tool permissions, model telemetry.
Cybersecurity
Broad enterprise IT cybersecurity covering network perimeters, cloud infrastructure, endpoints, identity systems, and 24/7 SOC operations.
Zero Trust architecture, SIEM/SOC telemetry, EDR, network hardening.
Sovereign AI
Total data residency and infrastructure control for regulated bodies—private LLMs, air-gapped clusters, and sovereign model custody.
Air-gapped enclaves, private weight hosting, local vector indexing.
AI Solutions
Design, development, and scaling of custom enterprise AI applications, agentic workflows, and intelligent business automations.
Workflow orchestration, ERP/CRM integration, multi-agent frameworks.
Not sure where your organization stands on AI security & governance?
Take our comprehensive assessment to identify security gaps, evaluate data privacy readiness, and receive a prioritized implementation roadmap.
Secure Your Enterprise AI Ecosystem
AppXcess AI security services cover your models, enterprise data, applications and autonomous agents: runtime guardrails, access controls and the audit record your governance programme runs on. Start with an assessment of where your AI estate stands today.